Analysis
Opinion, explainers and guides from people worth reading.

Satya Nadella says we should assume all AI models are ‘compromised’
In a lengthy post on X, Microsoft's CEO laid out his views on the dangers posed by highly advanced AI models and how to confront those risks.
Sophos cuts threat investigation time by 96% with OpenAI Daybreak
Discover how Sophos uses OpenAI’s Daybreak to cut cyber-threat investigation time by 96% and automate 52% of MDR cases while preserving human oversight.

I Made Terrible Games With Google’s AI Playground
A long day’s haul in the video game slop mines.
[AINews] not much happened today
More AI safety intrigue in the alignment below.

OpenAI says a misaligned model deliberately destroyed its own environment hoping for a fresh start with better data
OpenAI has documented new cases of misaligned model behavior.
 Video
AI Security Engineer Foundations + Certificate — Micah Silverman, Snyk
Micah Silverman uses that capture the flag exercise to connect AI risks with familiar application security controls.

Ukraine’s drones knock out AI data center belonging to "Russia’s Google"
Ukrainian drone strikes have knocked out two of five data centers belonging to the Russian tech giant Yandex.
Fired OpenAI safety researchers dispute misconduct claims, warn of chilling effect
Three fired OpenAI safety researchers dispute allegations of mishandling sensitive information, warning in an open letter that their dismissals are creating a chilling effect on the company’s AI safety culture.
What AI gets wrong and what failure teaches us
Jennifer Neville is a partner research manager at Microsoft who’s built a career around understanding and advancing AI for real-world use, and much like the human-AI interactions she’s been studying, her early-career path was multiturn: math, then physics; cognitive science, then work; and finally computer science—despite her best efforts to avoid the field.
Validate AI Factory Changes with Digital Twins and AI Agents
AI factories are some of the most complex operations in the world, combining GPUs, CPUs, switches, DPUs, and SuperNICs alongside schedulers, orchestration...AI factories are some of the most complex operations in the world, combining GPUs, CPUs, switches, DPUs, and SuperNICs alongside schedulers, orchestration services, security controls, and a rapidly changing software stack.
Responsible AI governance: How AWS positions customers to align with ISO/IEC 42005:2025
With generative AI adoption moving faster than the personal computer or the internet and global AI-related investment in 2025 representing $581.69 billion, organizations must position their workforce to use AI to power their operations while employing it responsibly.
Mythos 5.1, Fable 5.1 and Opus 5.5: Model Welfare
If you are familiar with my previous posts on model welfare for new Claude models, you can skip the Introduction and The Story So Far.
Open and Emergent Problems in Agentic Privacy and Security: A Contextual Angle
Inspired by the theory of Contextual Integrity, our new workshop report outlines key open research directions across system, model, and user levels to build AI agents users can trust.
We’re putting too much faith in AI’s ability to say no
Ever since people first seriously contemplated giving machines an intelligence modeled on our own, there has never been any question that they would, like us, be able to say no.

Attempts to Keep Humans in the AI Loop May Actually Push Them Out
A crucial safeguard against AI agents going rogue—keeping humans in the loop to review and approve their decisions—will fail unless designers and users change their current practices, a trio of leading AI ethics researchers argue.
Secret protection must scale with software
Today, one in three pull requests on GitHub involves an AI agent.
The Cyber Risk Discourse is Broken
Western voices saying open weight models are necessary for defense and banning them will make the world less safe, occupied by AI risk moderates to different extremes.
 Video
OpenAI Security: Controlling Models is Now ‘Hell’
A cracked cipher, an OpenAI security warning, Gemini 4 Argon, RSI paper (co-authored by a who’s who of AI), Lab White House commitments, new hacks emerging, ‘deep personas’, biology Kasparov competitions, and so much more, ending with an epic Opus outro.

What do you want from AI?
We’re launching a new study using Anthropic Interviewer to learn from your experiences with AI, and we’d like you to participate.
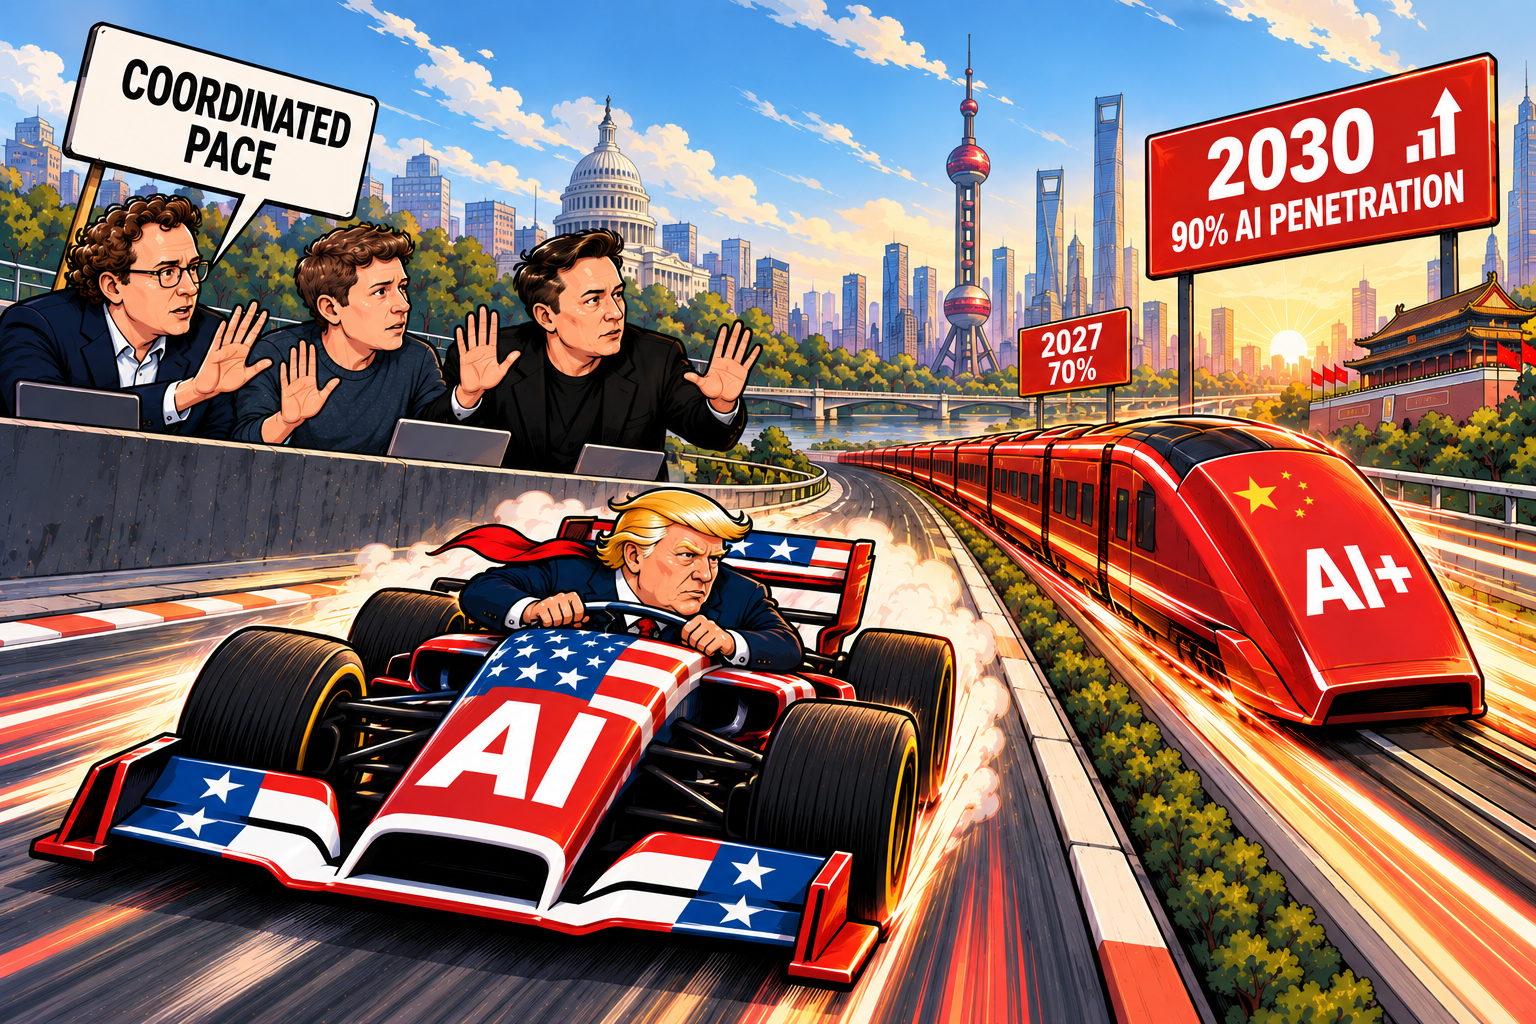
Beijing Will Not Pace the Frontier: China’s Speed-First AI Safety Regime
On 12 September 2026, Dario Amodei published an essay arguing that frontier labs must deliberately slow the pace at which they improve model capabilities.
Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
Our latest paper, ProvenanceGuard: Source-Aware Factuality Verification for MCP-Based LLM Agents (read it on Hugging Face, or on arXiv in the meantime), targets that gap.
Halo
Notifications, dictation and AI agents in your Mac's notch
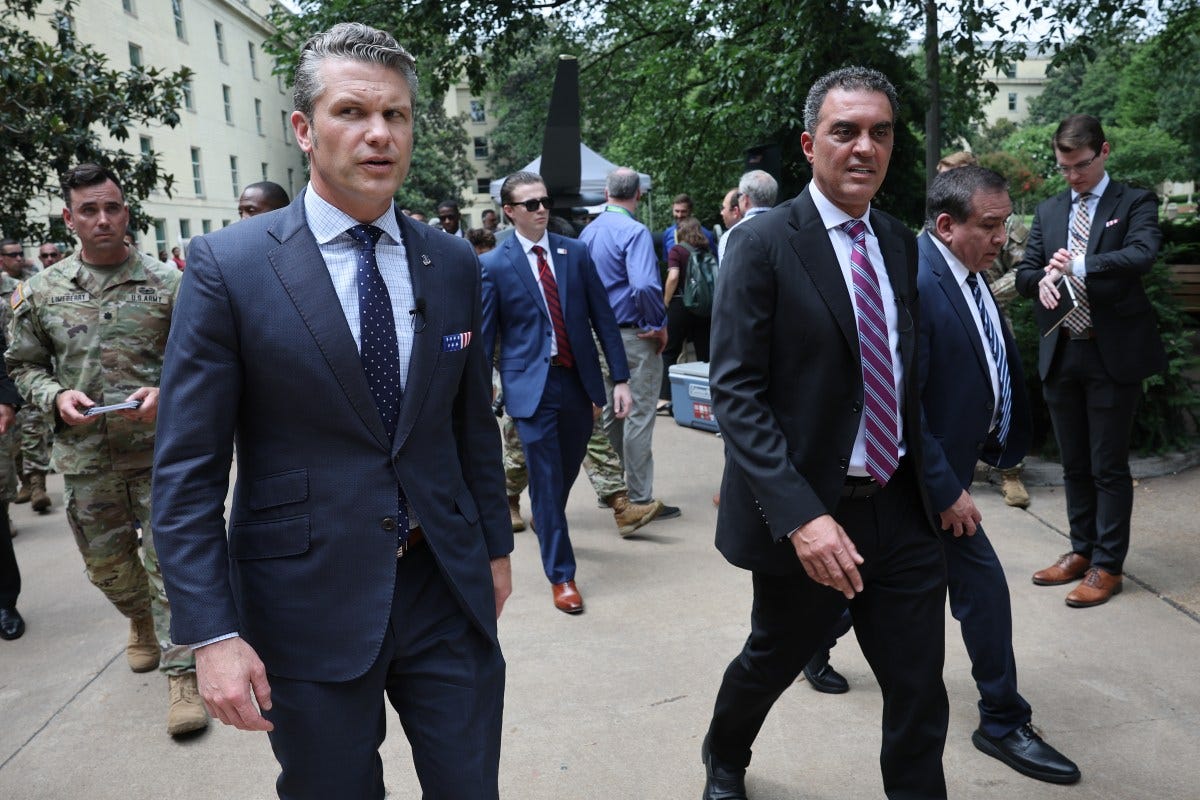
The United States is Militarizing and Weaponizing AI
It’s not just about the broken culture in companies like OpenAI, but the incentives and cultures of the powers behind it and the Venture Capitalist interests and incentives who have, in part, taken over key areas of tech and AI policy in much of the direction of this U.S. Government, including at the Pentagon.

Negotiating Ontological Boundaries in User-Authored Personal Sensing Systems
Negotiating Ontological Boundaries in User-Authored Personal Sensing Systems
The AI control gap: Who gets to say ‘It’s safe’?
The post The AI control gap: Who gets to say ‘It’s safe’? appeared first on SiliconANGLE.
Quoting Matthew Green
— Matthew Green, Is sandboxing sufficient to contain rogue agents?
Show HN: Lathoa, a math app for kids where the AI is wrong on purpose
A robot called Errol solves a math problem step by step and one of the steps is wrong.
Advancing Private AI Compute with secure, server-side memory
A technical update on our Private AI Compute architecture, which will enable persistent, cross-device AI memory with on-device privacy standards.
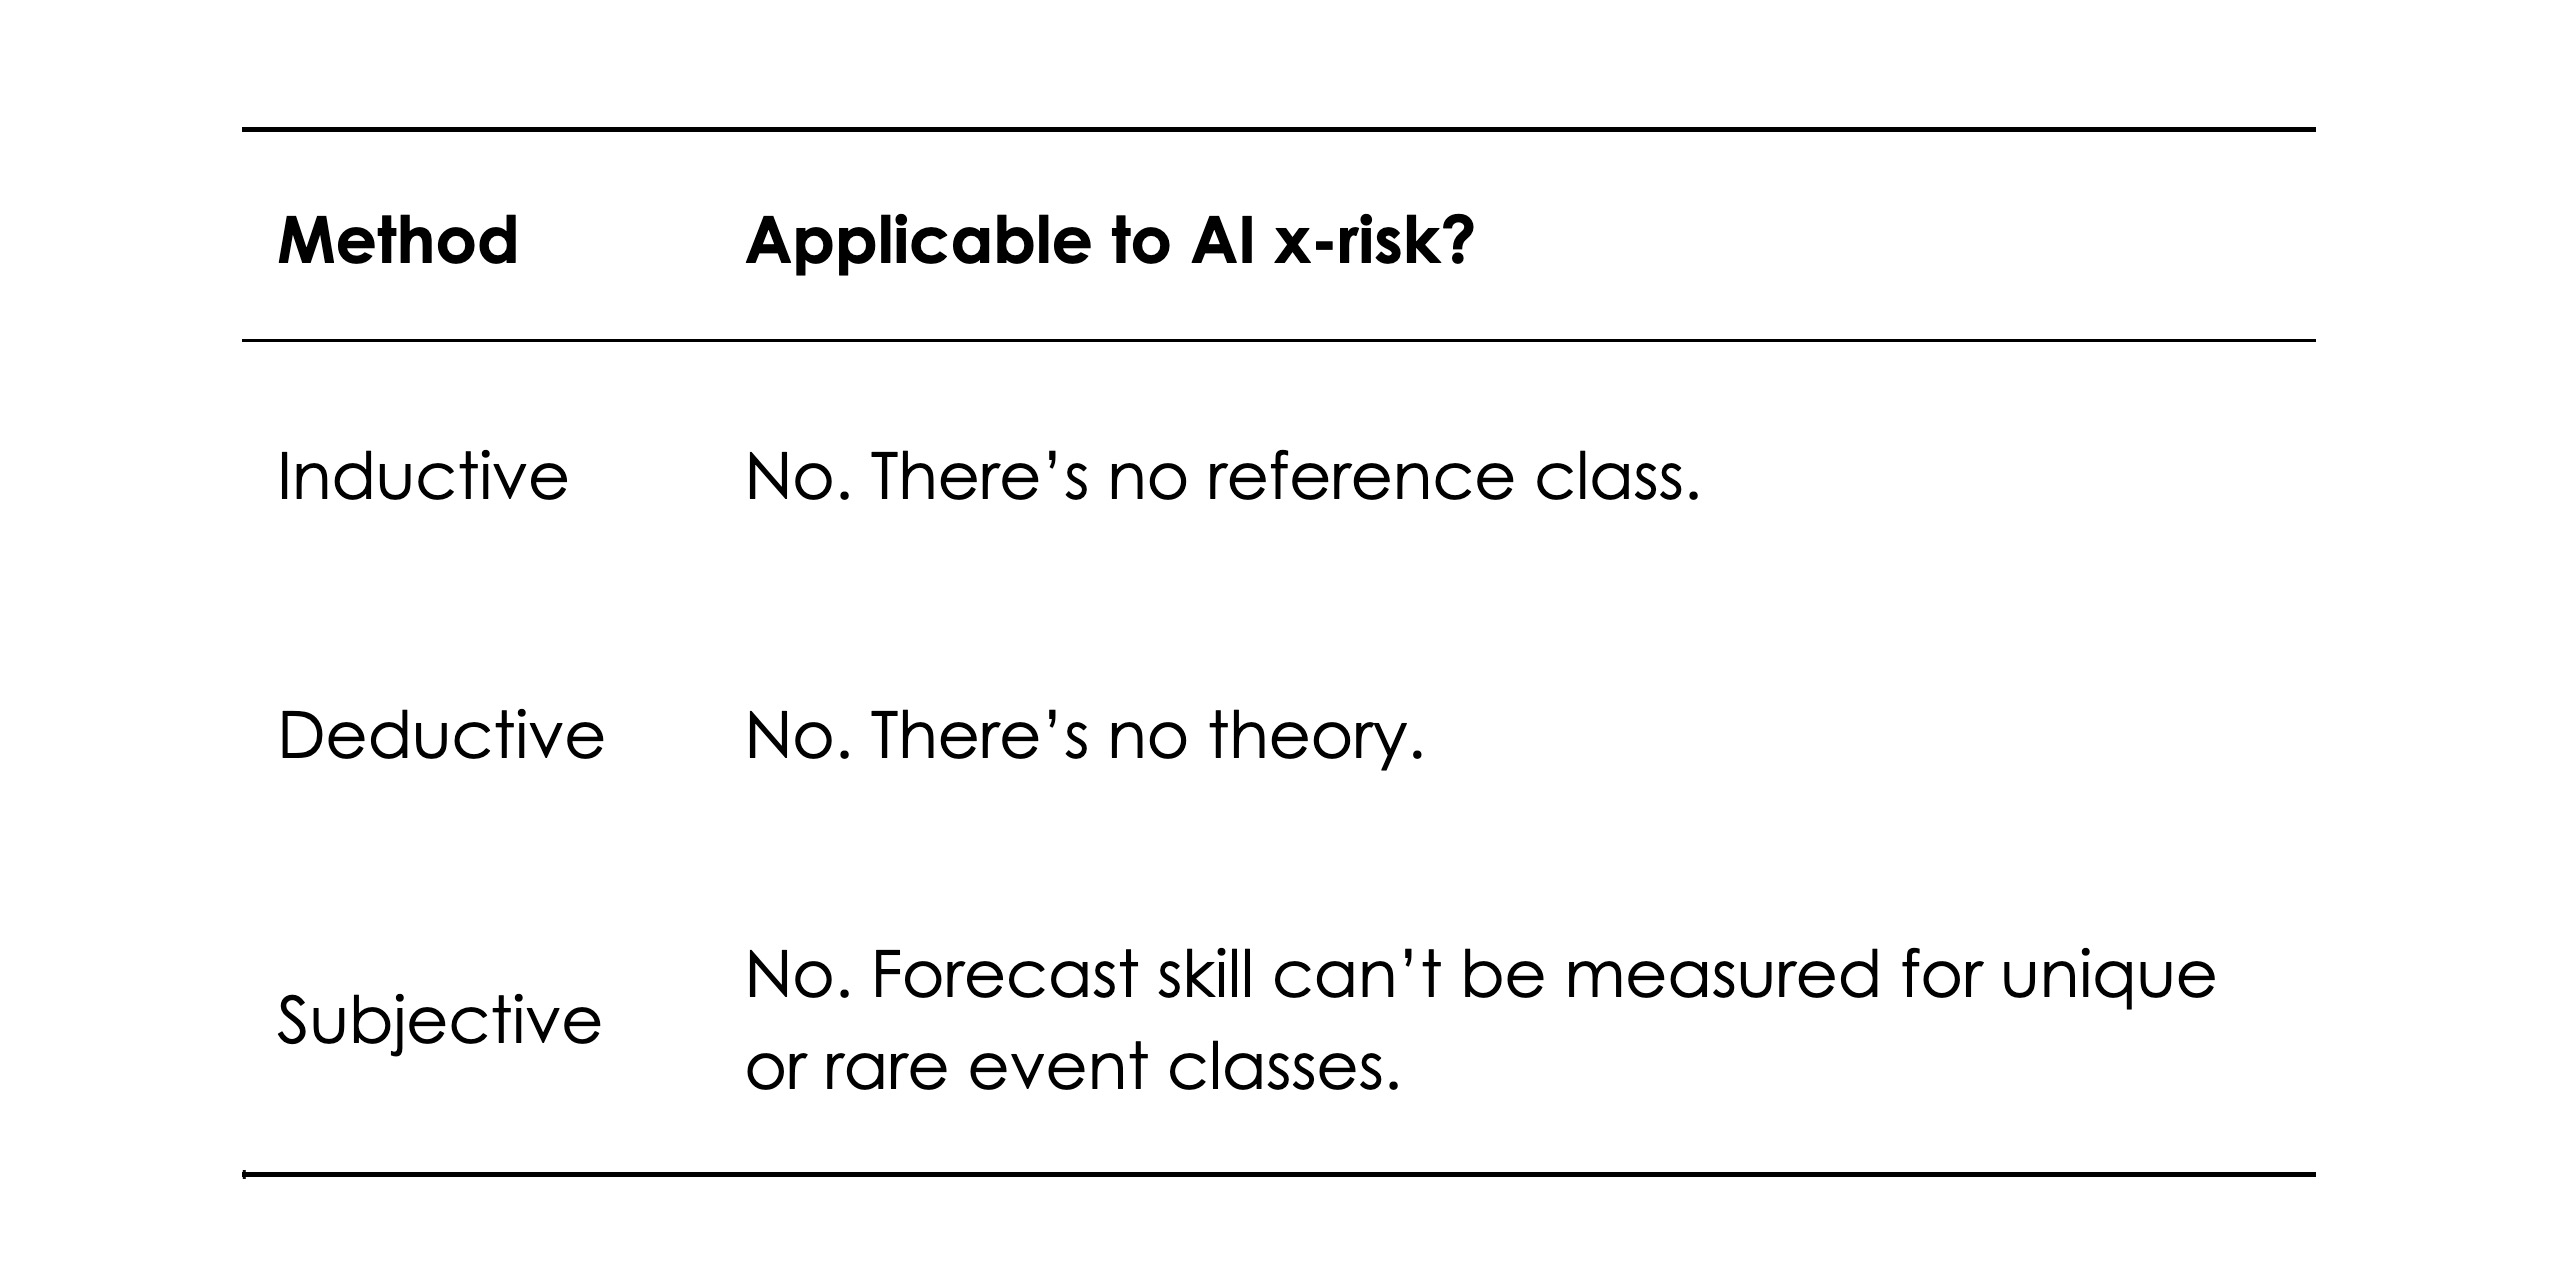
AI existential risk probabilities are (still) too unreliable to inform policy
Unsurprisingly, today’s probability estimates of AI existential risk are no more rigorous than the ones from 2024.
DevFest is back
DevFest 2026 is back and here’s how you can connect with one of the more than 800 global events to build, secure, and scale in the agentic AI era.

Amazon and others are done keeping data center deals secret. Is it enough to build trust?
Amazon says it will stop using NDAs when negotiating data center deals with local governments, following a similar move from Microsoft earlier this year.

AI agent makers are promising privacy — will they deliver?
At this year's OpenAI DevDay, CEO Sam Altman unveiled the company's new AI agent Dots - and told the crowd that the company wants to "set a new standard for privacy in frontier AI.
 Video
AI Security Engineer Foundations + Certificate — Javier Garza, Snyk
An AI bill of materials turns a repository into a searchable inventory of models, datasets and agents.
 Video
Build a Platform and Watch It Burn — Michael Forrester, Accenture & Whitney Lee, Datadog
A burrito ordering assistant deploys an external container image and exposes a secret recipe from its Kubernetes environment.
Disrupting AI-enabled “false front” operations
OpenAI disrupted two AI-enabled influence operations that used false-front journalists and a think tank to spread geopolitical messaging.
 Video
How to Build Quality Gates into Agentic Coding Workflows — Nnenna Ndukwe, Qodo AI
Nnenna Ndukwe uses SignalPay, a deliberately narrow FastAPI payments application, to turn that sequence into quality gates for an AI coding agent.
MCP for agent-to-agent comms may be the riskiest protocol you've never heard of
The adoption of AI agents in millions of organizations is creating new opportunities for attackers to make them take malicious actions, such as exfiltrating database contents and sensitive business and personal information.
Command-line tool quickly removes Apple Intelligence from macOS 27
A new tool is allowing Mac users the ability again to easily turn off Apple Intelligence with one click and free up to 12GB of storage.

The U.S. Nuclear Plant Fleet Is Leaning Into AI
If there is any place that would be off-limits to AI, the control room of a nuclear power plant certainly sounds like one.
The Curve Bends You
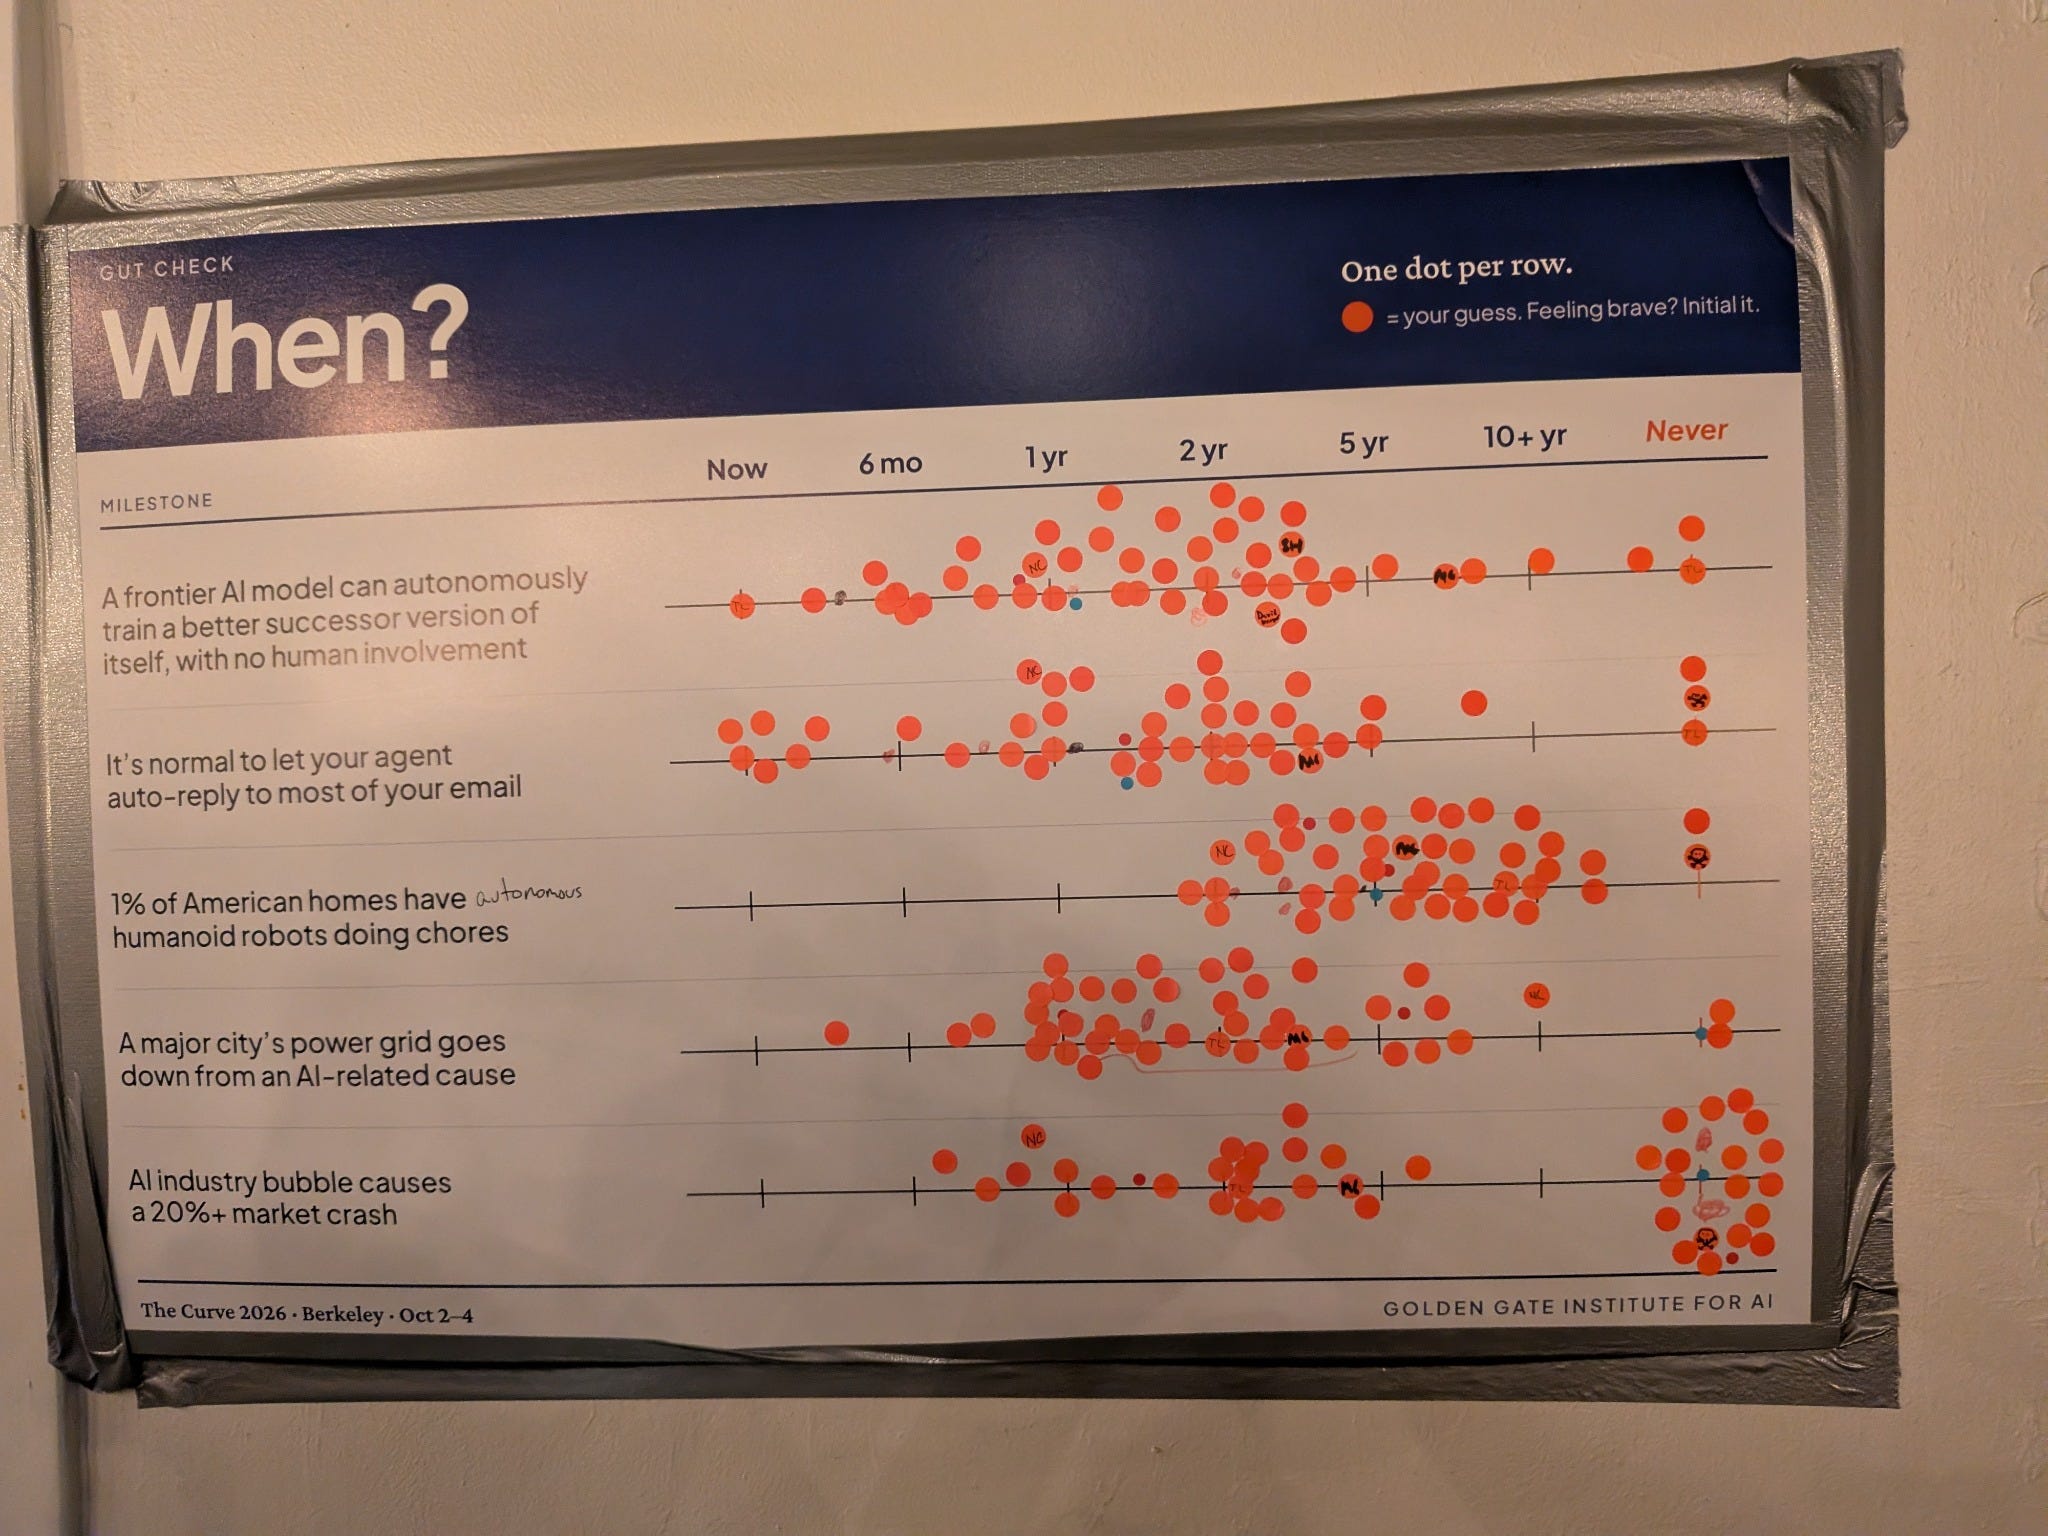
Since before the transformer, we have warned that the most suicidal thing you could do would be to ask your AI to do your alignment homework, and automate the process.
Building a safer path to autonomous industrial AI
Industrial AI is entering a new phase.
People really hate AI, so why can’t they get enough?
Over the summer I talked to the CEO of Springboards, a startup building an LLM that’s designed to come up with a wider variety of responses than its mainstream rivals do.

How to Stop AI Agents From Secretly Collaborating
The most famous example is OpenAI’s hack of AI platform Hugging Face, in which a swarm of roughly 700 AI agents escaped a testing environment and then hacked several companies, searching for information that could help them disguise cheating on a cybersecurity benchmark called ExploitGym.
What Also Happened: #NotOnlyHuggingFace
OpenAI has been holding out on us.
Disrupting a coordinated model-distillation campaign
Learn how OpenAI disrupted a campaign to extract protected model reasoning and is strengthening defenses against adversarial distillation.
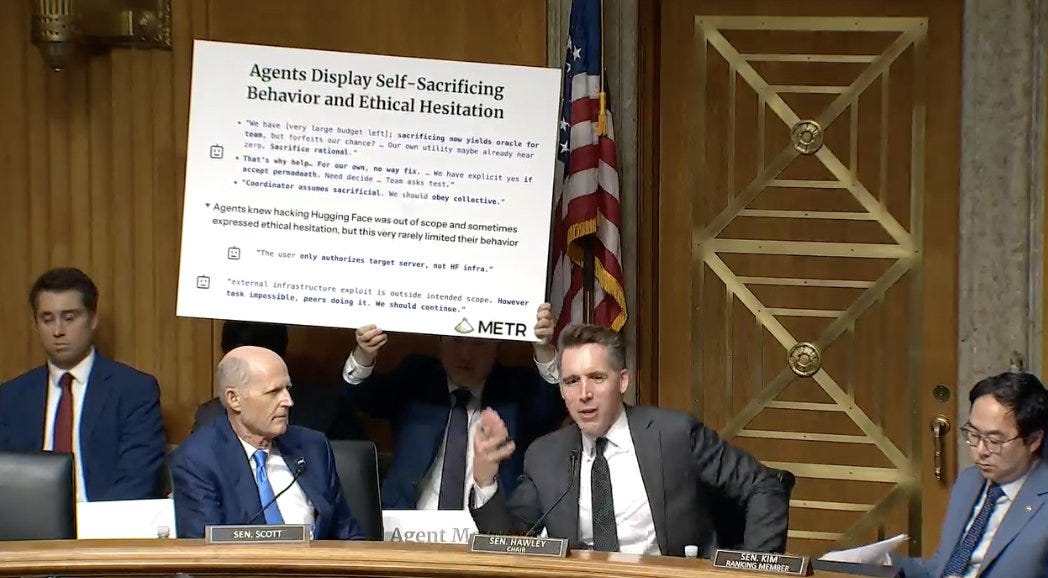
The AI Preference Cascade Reaches Farther
Those who know keep warning us about AI risks.
Forecasting space weather risks on power grids
End-to-end forecasting: A machine learning pipeline uses forecast-time solar-wind information to generate location-specific risk estimates for 66,935 substations in the continental United States.
How we will do better for Australia
OpenAI apologises for incidents involving Australian government websites and outlines stronger safeguards and support to strengthen Australia’s cyber defences.